Velocity Labs

Ruby on Rails code audit

A Rails code audit from people who've been building Rails since 2007.

Most of the apps we audit are Rails apps, often inherited, rushed to launch, or partly written by AI. We review yours against the problems Rails apps actually have, and tell you in plain English which ones matter and what to fix first.

What a Rails code audit checks

Every Rails audit covers the eight areas in every code audit, plus checks written for Rails itself.

  • Who can see whose data

    Record lookups that aren’t scoped to the signed-in user, admin areas and mounted engines (Sidekiq, Active Admin) without authorization, and tenant data that leaks between accounts.

  • Sign-in, sessions, and secrets

    Devise or hand-rolled authentication, brute-force protection, cookies and CSRF, and credentials, secret_key_base, or API keys committed to the repo.

  • Injection and unsafe input

    Mass assignment through strong parameters, SQL built from strings in Active Record, html_safe and raw in views, open redirects, and file uploads through Active Storage.

  • Data that holds up

    Validations with no database constraint behind them, callbacks with side effects, race conditions, risky migrations, and background jobs that charge a card twice when they retry.

  • Speed under real traffic

    N+1 queries, unbounded queries and missing pagination, caching, slow work in the request, and Puma, Sidekiq, and connection pool settings that don’t fit together.

  • Version and upgrade path

    Whether your Rails and Ruby versions still get security fixes, the gap between your Rails version and its framework defaults, and the gems that will block the next upgrade.

More than a Brakeman report

Every audit runs Brakeman, bundler-audit, and RuboCop Rails against your code, but scanners only find the patterns they know. The findings that hurt most in Rails apps are usually ones a scanner can’t see:

  • A find that should have been current_user.projects.find
  • A Sidekiq dashboard mounted without a login
  • A uniqueness validation with no unique index
  • A job that sends a customer email again on every retry

Those come from reading the code, and from having fixed the same problems in our own Rails apps for almost twenty years.

Rails code audit pricing

Three levels, each a fixed fee. Essentials covers the most important Rails checks; Standard and Comprehensive cover all of them. See everything every audit includes.

Essentials

A fast health check

$1,000 fixed fee

Best for: Answering "is this codebase OK?" before you buy, hire, or launch.

  • Review of your code, configuration, CI, and database schema
  • Automated scans for security issues, vulnerable and outdated dependencies, leaked secrets, and code quality
  • The essential checks for each technology in your stack
  • Critical and high findings written up in full
Order Essentials

Comprehensive

Due diligence depth

$2,500 fixed fee

Best for: Acquisitions and technical due diligence, compliance preparation, or after an incident.

Everything in Standard, plus:

  • Line-by-line review of sign-in, payments, and data access
  • Steps to reproduce every finding
  • Your public website: accessibility, search visibility, and security headers
  • Domain and email setup: DNS, SPF, DKIM, and DMARC
Order Comprehensive

Is your Rails version still supported?

Rails supports each release with security fixes for about two years, so many apps are running an end-of-life version that no longer gets them. Every Rails audit checks your Rails and Ruby versions against the official maintenance policy.

If you’re behind, the report lays out the upgrade one version at a time, and Standard and Comprehensive also list the gems and deprecations that stand in the way. When you’re ready, we can do the upgrade too.

Rails support today Latest: 8.1.4.1
  • Rails 8.1 Supported
    Bug fixes
    Until Rails 8.2 ships
    Security fixes
    Until Oct 10, 2027
  • Rails 8.0 Unsupported
    Bug fixes
    Ended May 7, 2026
    Security fixes
    Ended Nov 7, 2026
  • Rails 7.2 Unsupported
    Bug fixes
    Ended Aug 9, 2025
    Security fixes
    Ended Aug 9, 2026
  • Rails 7.1 and older Unsupported
    Bug fixes
    Ended by Oct 1, 2024
    Security fixes
    Ended by Oct 1, 2025

Checked November 13, 2026 against the Rails maintenance policy.

Rails apps we've audited and kept running

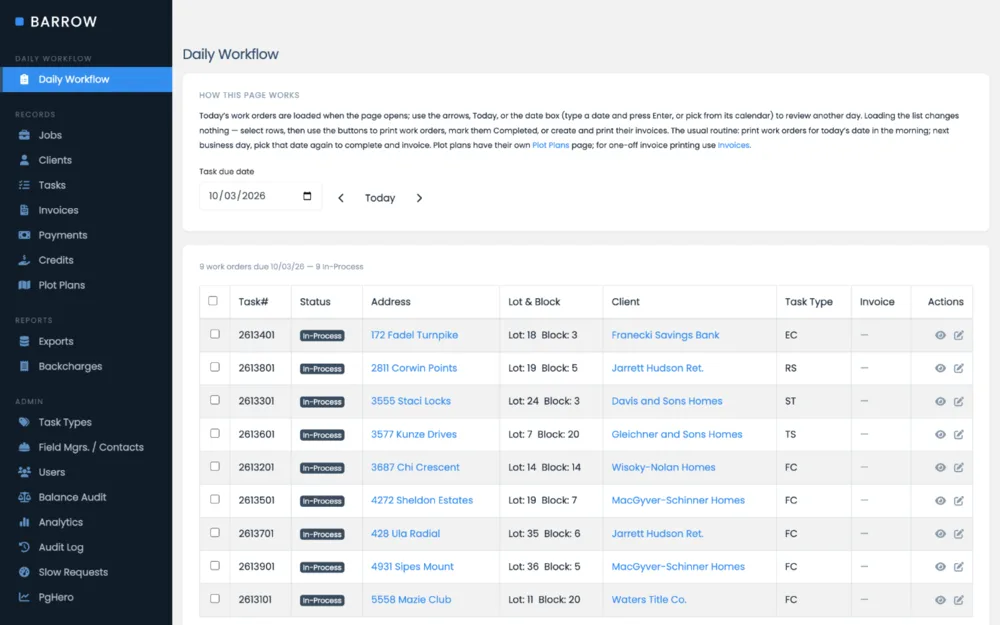
The surveying firm's daily workflow screen, listing the day's work orders

Land surveying firm

We audited this firm's job and invoicing app, fixed the three urgent issues we found, rebuilt its invoice engine, upgraded Rails, and still look after it.

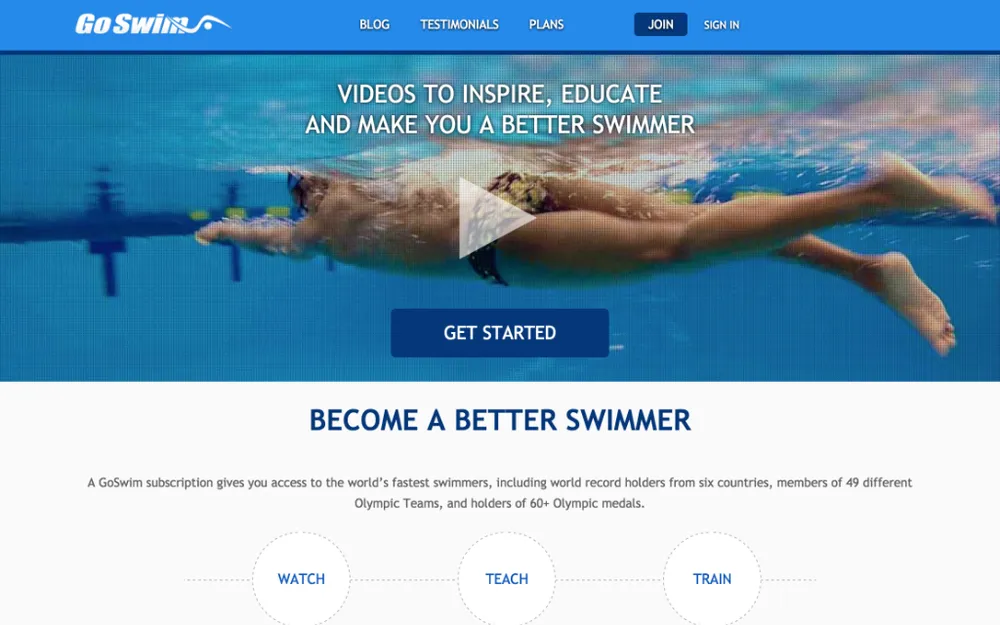
Go Swim home page: videos to inspire, educate and make you a better swimmer

Go Swim

A swim instruction video site we took over after launch and developed for six years: subscriptions, payments, and video delivery.

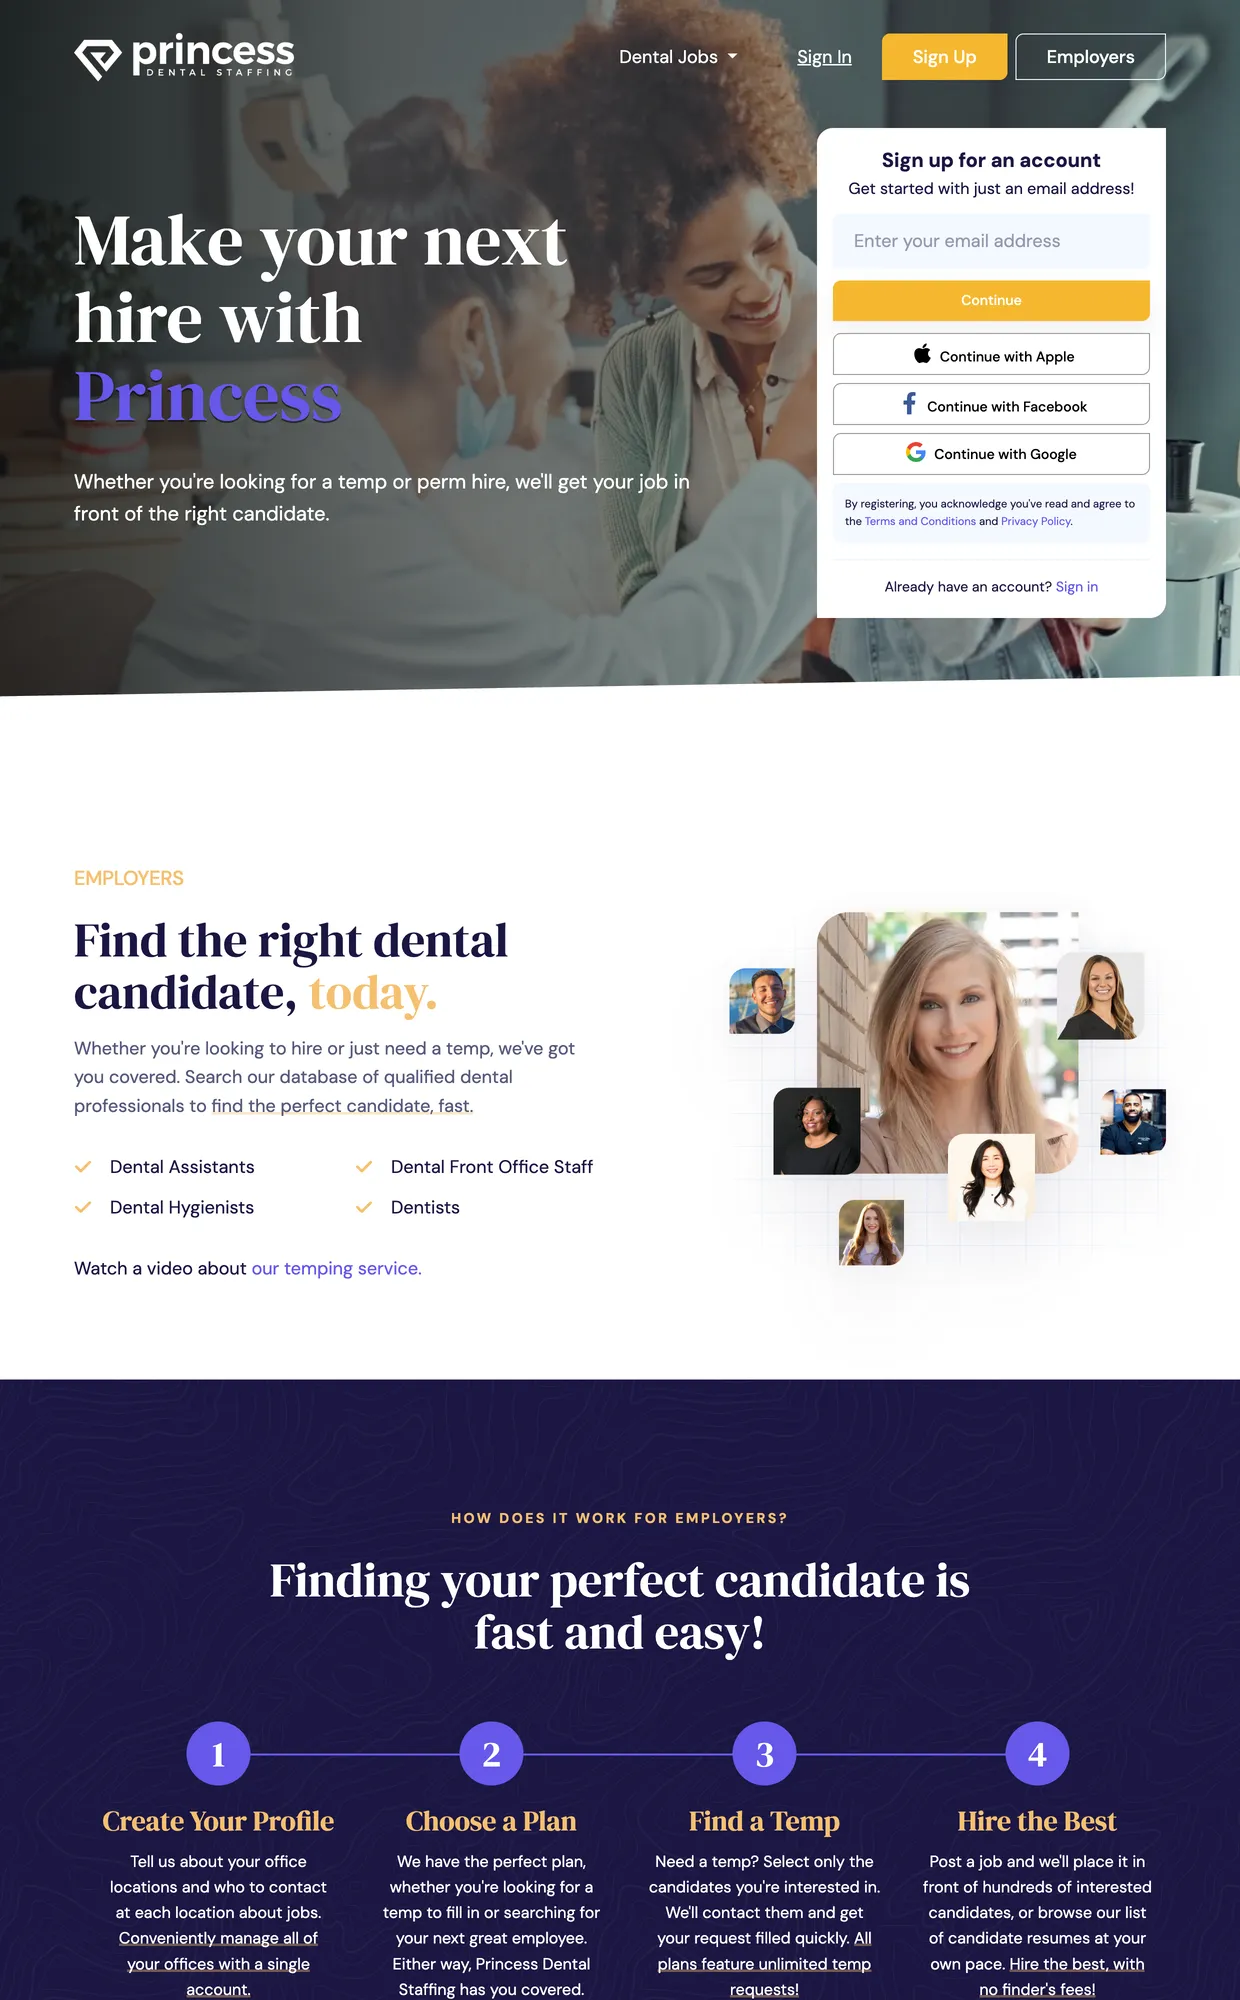
Princess Dental Staffing home page: Make your next hire with Princess

Princess Dental Staffing

Dental practices use it to hire staff and book temps online. Along the way we built its Stripe subscriptions, the API behind its mobile app, and AI-based matching, as it grew from one local market to nationwide.

Questions about Rails code audits

How much does a Rails code audit cost?

The same fixed fees as every audit: $1,000 for Essentials, $1,500 for Standard, and $2,500 for Comprehensive. Compare the levels. Hire us for hourly development within 30 days of your report and up to $1,000 of the fee comes off your first invoice.

Is a Rails security audit included?

Yes. Every Rails code audit includes a security audit: data access, admin areas, sign-in, sessions, secrets, injection, and file uploads, checked against the known weaknesses of Rails, plus Brakeman and bundler-audit scans.

Which versions of Rails do you audit?

Any of them, from apps that have been running on an old version for a decade to apps on the latest release. If you’re behind, the report says how far and lays out the upgrade one version at a time; Standard and Comprehensive also list the gems that stand in the way.

Can you audit a Rails API with a React or mobile front end?

Yes. API-only Rails apps get the same review, with extra attention to authentication tokens, CORS, and what each endpoint returns. If the front end is part of the audit, it gets its own checks for React, Next.js, or React Native.

Do you need to run our app?

Essentials reviews the code without running it. Standard and Comprehensive boot your app and run your tests in an isolated, disposable environment. Either way, we never connect to your production servers, databases, or accounts.

Can you fix what the audit finds?

Yes. We’ve been maintaining and upgrading Rails apps since 2007. We can work alongside your team or take it on ourselves, and the audit credit applies.

Order a Rails code audit

Tell us about your Rails app and we'll recommend the level that fits.

Prefer to talk first? Book a 30-minute call